ISO 27001 Audit, Implementation & Certification Services in Pune, India.
Build, implement and improve an Information Security Management System (ISMS) with a practical, risk-based approach. Varutra supports organizations across India with ISO/IEC 27001:2022 gap assessment, risk assessment, ISMS design and documentation, control implementation, training and awareness, internal audit and certification readiness.

ISO 27001 Gap Assessment
Identify ISMS, control and evidence gaps against ISO/IEC 27001:2022.
ISO 27001 Risk Assessment
Identify and evaluate information-security risks within the ISMS scope.
ISO 27001 Control Implementation
Implement risk-based security controls aligned with the ISMS and Annex A.
ISO 27001 Gap Remediation
Prioritize and address remaining gaps to strengthen ISO 27001 readiness.
ISMS Documentation
Develop policies, procedures, registers, SoA and supporting evidence.
Certification Readiness
Prepare controls, evidence and teams for independent certification audits.
ISO 27001 Implementation Guide
Use a structured implementation roadmap to understand scope, risk assessment, policies, controls, evidence, internal audit and certification readiness before starting your project.
What Is ISO/IEC 27001:2022?
ISO/IEC 27001:2022 is an international standard for establishing, implementing, maintaining and continually improving an Information Security Management System (ISMS). It gives organizations a structured way to understand information-security risks, select appropriate controls and demonstrate that security is governed as an ongoing management process.
ISO/IEC 27001:2022 is not simply a checklist of technical controls. An effective ISMS connects leadership, people, processes, technology, risk management, documentation, evidence and continual improvement. The applicable Annex A controls are selected based on the organization's risk treatment and documented through the Statement of Applicability.
ISO 27001 Compliance / Implementation
- Define ISMS scope, context, interested parties and objectives
- Establish risk assessment and treatment processes
- Design applicable policies, procedures and security controls
- Generate evidence and operate the ISMS before audit
ISO 27001 Certification
- Independent certification-body assessment of the ISMS
- Stage 1 review of documented ISMS readiness
- Stage 2 assessment of implementation and effectiveness
- Certificate issued by the independent certification body
What Does an ISO 27001 ISMS Help You Manage?
An ISO/IEC 27001:2022 ISMS provides a risk-based framework to manage information security, cybersecurity and privacy-related risks across people, processes, technology and third parties.
Information & Privacy
Protect confidential, personal, financial and business-critical information throughout its lifecycle while addressing relevant privacy risks.
Cybersecurity & Threats
Identify and treat cybersecurity risks affecting systems, networks, applications, endpoints and information assets.
Identity & Access
Manage authentication, authorization, privileged access and access governance to reduce unauthorized access risks.
Technology & Cloud
Address security risks across cloud services, infrastructure, applications, networks, endpoints and technology operations.
People & Third Parties
Manage security responsibilities, awareness and risks arising from employees, suppliers, vendors, partners and outsourced services.
Resilience & Continuity
Strengthen incident response, backup, recovery, availability and business continuity as part of a resilient ISMS.
A Structured Approach to ISO 27001 Readiness
Our ISO 27001 approach takes organizations from understanding their current information-security posture to establishing, operating and independently assessing an effective Information Security Management System (ISMS).
ISO 27001 Gap Assessment & Remediation
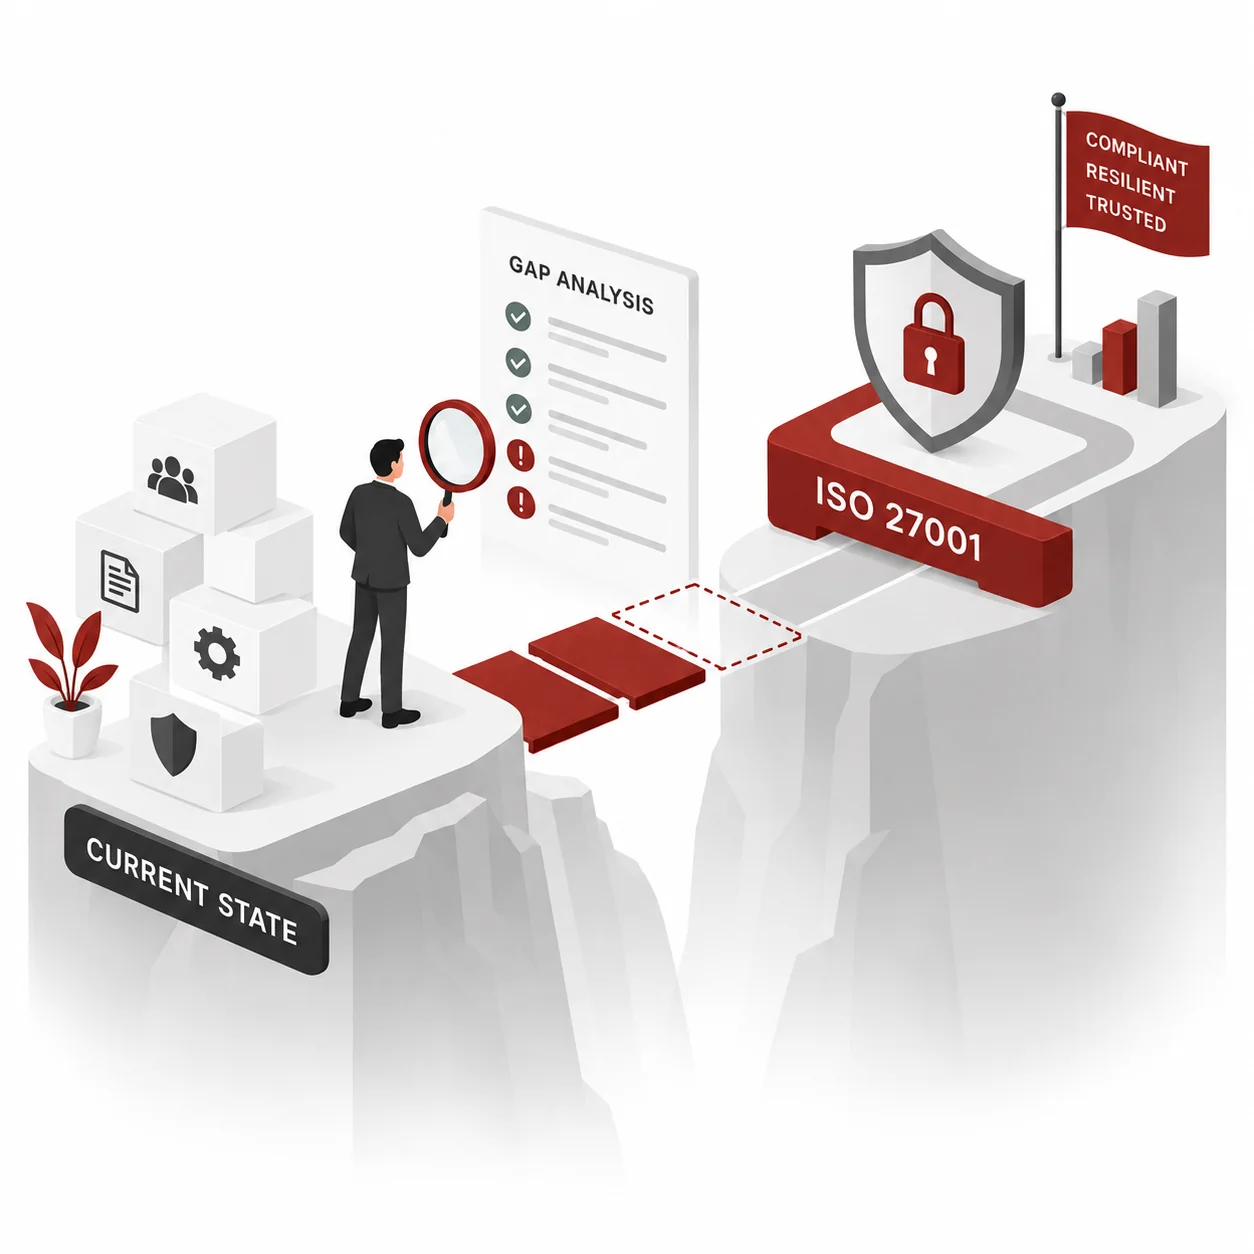
Identify compliance gaps and establish a clear path to ISO 27001 readiness. We assess your existing information security governance, processes, controls, documentation and evidence against applicable ISO/IEC 27001:2022 requirements.
We map identified gaps to the relevant ISMS requirements and Annex A controls, prioritize remediation needs and develop a practical roadmap to strengthen your information security management system and certification readiness.
Information Security Risk Assessment
Establish a risk-based foundation for your ISMS. We help identify information-security risks within the defined ISMS scope, evaluate their potential impact and likelihood, and establish appropriate risk treatment decisions.
The process can cover assets and information, threats, vulnerabilities, existing controls, business impact, risk criteria, risk ownership, treatment actions and residual risk. The results provide the basis for control selection and the Statement of Applicability.
ISMS Design & Documentation / Policy Drafting
Design an ISMS that reflects your organization's scope, risks and operating environment. We help establish the governance framework and documented process required to manage information security systematically.
Depending on the organization's scope and requirements, this can include ISMS scope definition, Information Security Policy, supporting policies and procedures, risk assessment methodology, Risk Treatment Plan, Statement of Applicability, objectives, roles and responsibilities, control documentation and evidence requirements.
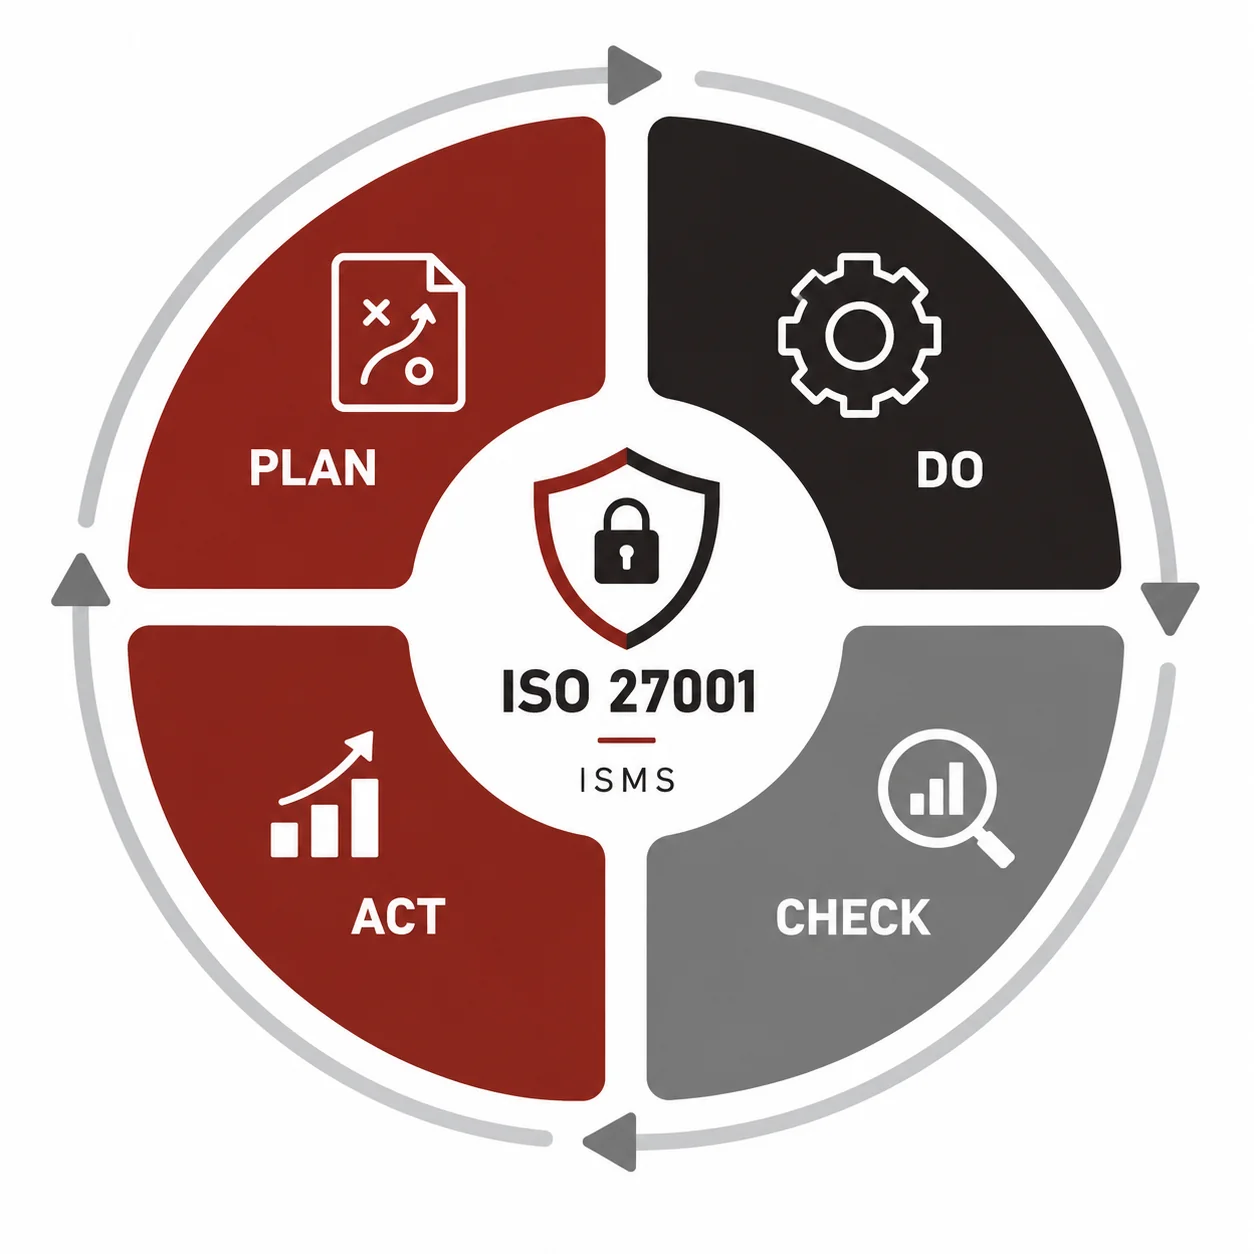
ISO 27001 ISMS Implementation
Turn the documented ISMS into an operating management system. We work with stakeholders and control owners to implement applicable information-security processes, controls, responsibilities and evidence mechanisms.
Implementation may address areas such as access management, asset management, information classification, supplier security, incident management, vulnerability management, logging and monitoring, business continuity, physical security and other controls determined by the organization's risk assessment and Statement of Applicability.
Training & Security Awareness
Embed information-security responsibilities across the organization. We provide awareness and role-based training to help employees, managers and control owners understand their responsibilities within the ISMS.
Training can cover information-security policies, acceptable use, secure information handling, incident reporting, access security, security responsibilities, audit evidence expectations and role-specific control requirements. Awareness activities can be aligned with organizational roles and the defined ISMS scope.
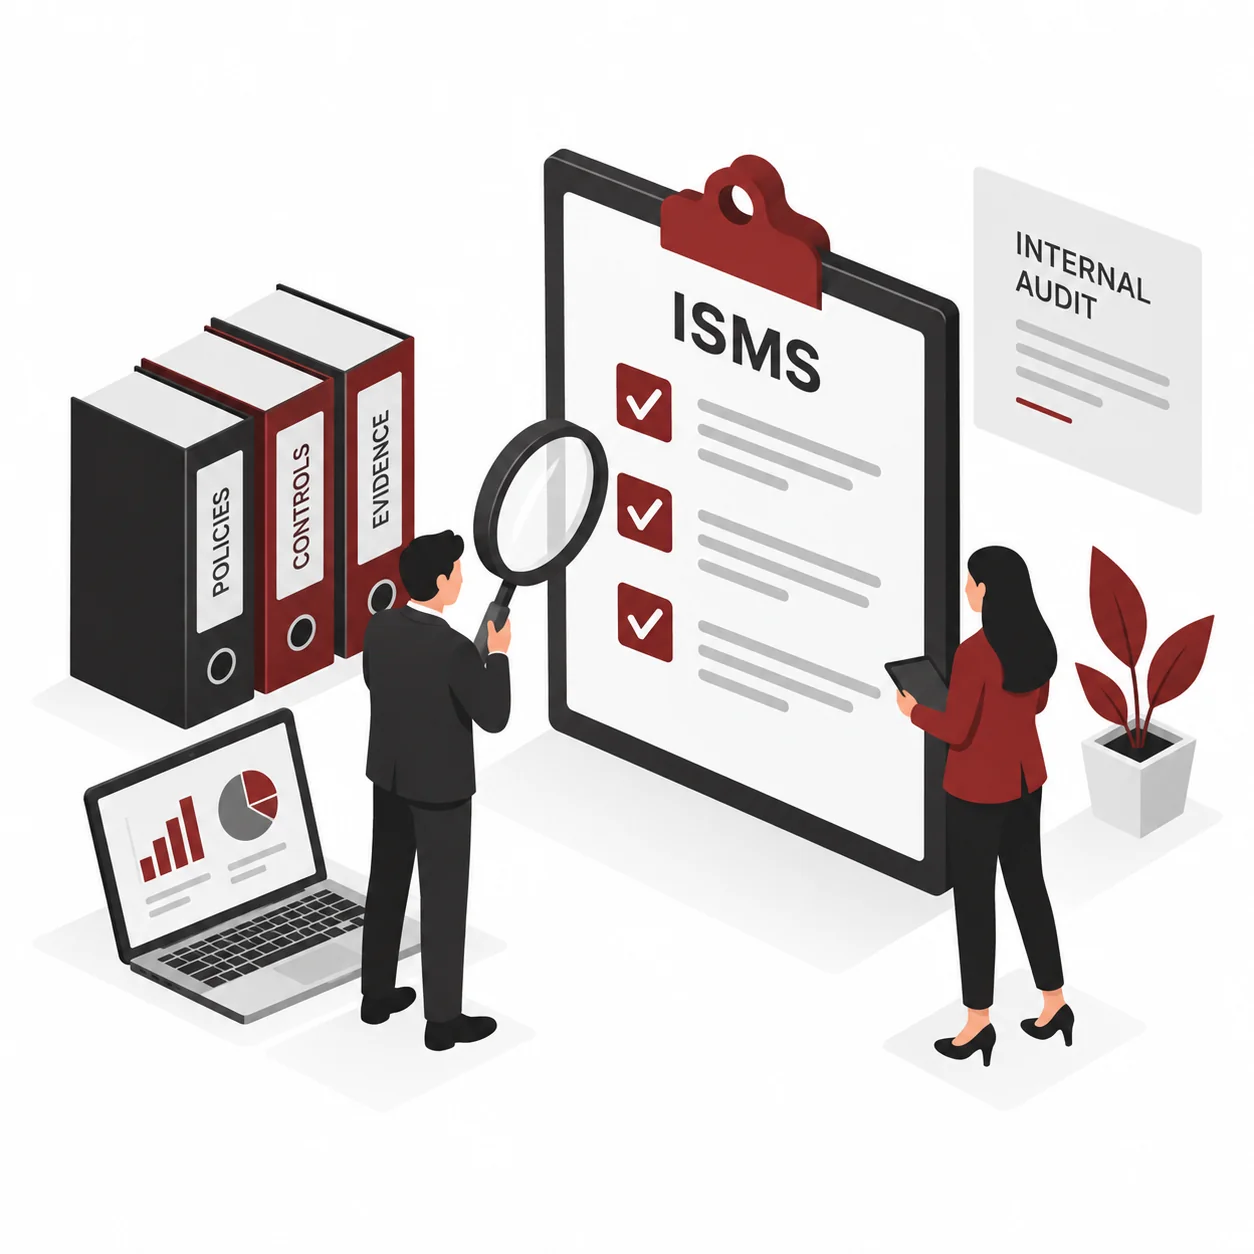
ISO 27001 Internal Audit
Validate the ISMS before the independent certification audit. We assess whether the implemented ISMS conforms to applicable ISO/IEC 27001 requirements and whether relevant processes and controls are operating as intended.
Internal audit activities can include audit planning, interviews, document and evidence review, control testing, process verification, finding identification, nonconformity reporting and corrective-action tracking. Management review preparation can also be supported where required.
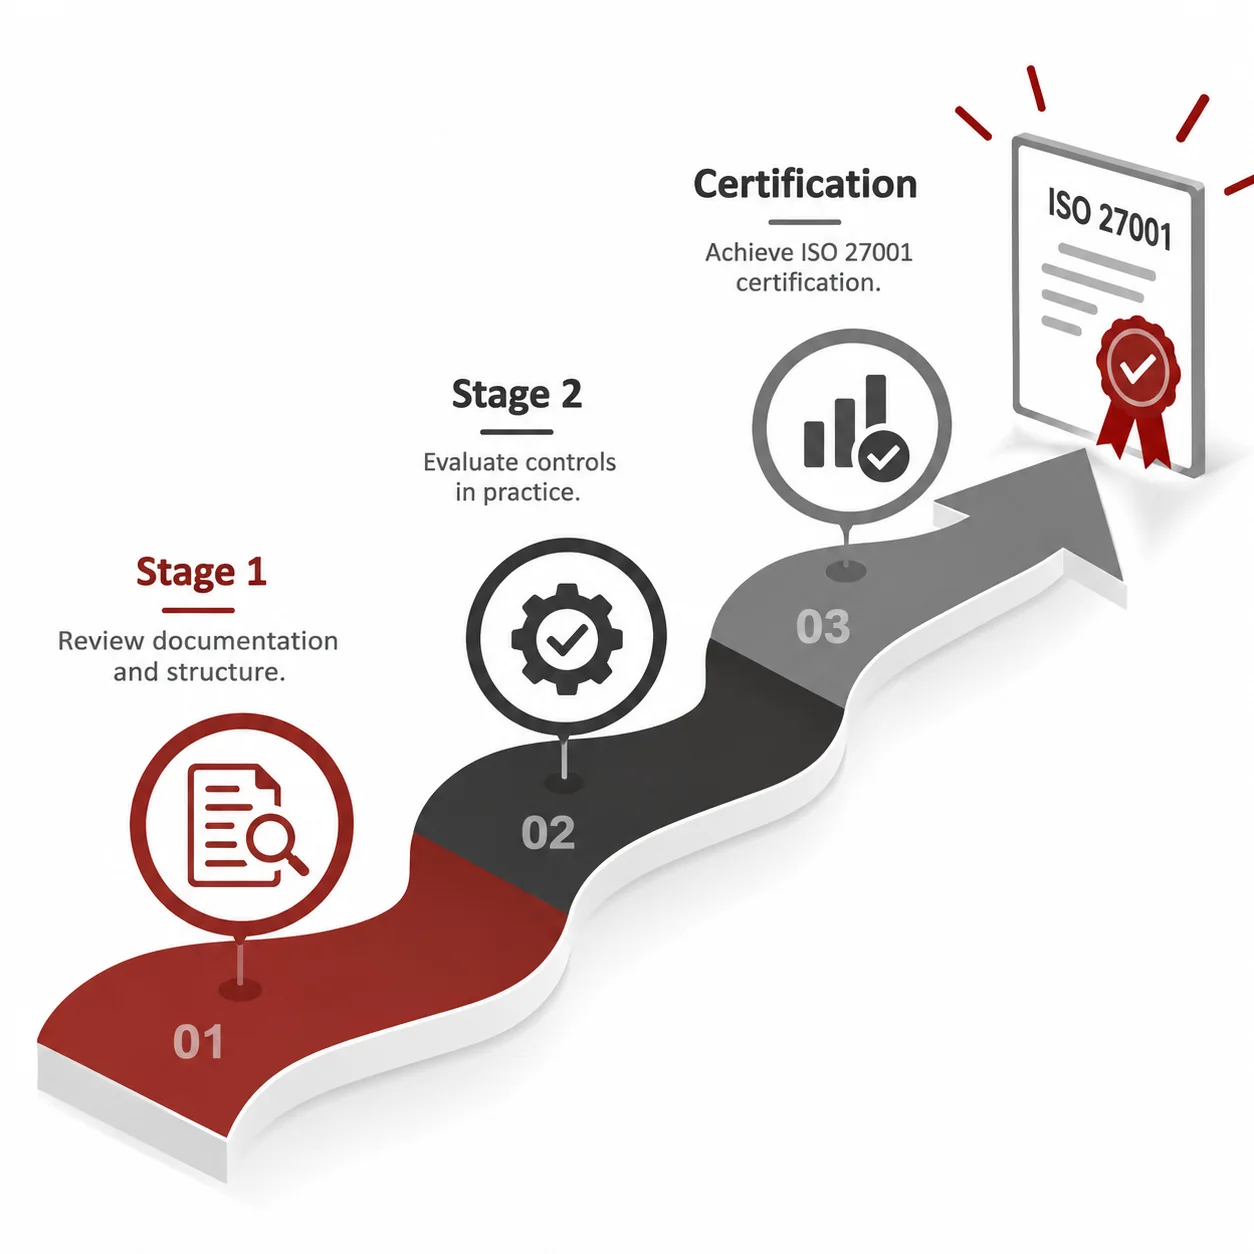
ISO 27001 Certification Readiness & Audit Support
Prepare your organization for independent ISO 27001 certification. We help bring together the ISMS documentation, risk treatment, controls, responsibilities and evidence required for the external certification assessment.
Support can include Stage 1 documentation-readiness preparation, Stage 2 implementation-readiness preparation, evidence coordination, audit preparation, finding analysis and corrective-action planning. The ISO 27001 certificate itself is issued by the independent certification body.
ISO 27001 Aligned to the ISMS Ecosystem
ISO/IEC 27001:2022 is the requirements standard for an ISMS. Supporting standards and frameworks can provide additional guidance depending on your objectives, scope and risk environment.
ISO/IEC 27001:2022
Defines requirements for establishing, implementing, maintaining and continually improving an Information Security Management System.
View ISO standardISO/IEC 27002:2022
Provides a reference set of information-security controls and implementation guidance that can support control design and improvement.
View ISO 27002ISO/IEC 27005
Supports information-security risk management and can inform risk identification, analysis, treatment and monitoring activities.
Explore ISO 27005From Security Gaps to Audit-Ready Evidence
Deliverables are tailored to the agreed ISMS scope and maturity. The objective is to create a working management system-not just documentation that exists only for the audit.
Practical ISO 27001 Readiness & ISMS Outcomes
We translate ISO/IEC 27001:2022 requirements into defined risks, controls, responsibilities and documented evidence-helping your teams implement, operate and continually improve the ISMS.
Discuss Your ISO 27001 ScopeISO 27001 Gap Assessment Report
Current-state findings, evidence observations and prioritized remediation actions.
Risk Register & Treatment Plan
Documented information-security risks, treatment decisions, owners and status.
ISMS Policy & Procedure Set
Scope-relevant governance documents, policies and operating procedures.
Statement of Applicability
Traceability for applicable controls, implementation status and rationale.
Internal Audit Report
Audit observations, conformity findings, nonconformities and corrective actions.
Certification Readiness Pack
Evidence coordination and readiness support for the independent certification audit.
Why Choose Varutra for ISO 27001 Consulting?
Varutra combines information-security consulting, cybersecurity assessment and GRC expertise to connect ISO 27001 requirements with your technical and operational environment. Our Audit & Compliance practice supports ISO 27001 implementation, gap assessment, risk assessment, internal audit, training, documentation and ongoing ISMS improvement.
Risk-Based ISMS Design
Translate business and information-security risks into treatment decisions, control ownership and practical ISO 27001 implementation priorities.
Cybersecurity + GRC Context
Connect ISO 27001 governance with vulnerability management, application security, infrastructure security and security operations.
Practical ISMS Implementation
Build operating processes, responsibilities, evidence and review practices that help the ISMS remain effective and continually improve after certification.
ISO 27001 Audit Readiness
Prepare documentation, evidence, control owners and corrective actions for the independent ISO 27001 certification assessment.
India-Focused Compliance Context
Where applicable, align ISO 27001 security governance with Indian regulatory, contractual, customer and sector-specific security requirements.
Certified & Experienced Professionals
Work with experienced cybersecurity, information-security and GRC professionals supporting ISO 27001 implementation, assessment, audit readiness and compliance.
ISO 27001 in the Broader Compliance Landscape
ISO 27001 can provide an information-security governance foundation that may support customer, contractual, regulatory and assurance requirements. Exact applicability depends on your organization, sector, data and scope.
Frequently Asked Questions About ISO 27001
Answers to common questions about ISO 27001 certification, consulting, ISMS implementation, risk assessment, internal audit and certification readiness in India.
ISO/IEC 27001:2022 is an international standard that specifies requirements for establishing, implementing, maintaining and continually improving an Information Security Management System (ISMS). It provides a risk-based management framework for protecting information and managing information-security risks.
ISO 27001 certification means an independent certification body has audited an organization's ISMS against the applicable ISO/IEC 27001 requirements and determined that it conforms to the certification criteria. Consultants can prepare and support the organization, but the certificate is issued by the independent certification body.
ISO 27001 consulting can include ISMS scoping, gap assessment, risk assessment, risk treatment planning, Statement of Applicability support, policy and procedure development, control implementation, training and awareness, internal audit, management review readiness, corrective-action support and certification audit preparation.
An ISO 27001 gap assessment compares an organization's current information-security governance, processes, controls and evidence against the applicable ISO/IEC 27001:2022 requirements. The outcome typically includes identified gaps, risk or priority context, evidence observations and a practical remediation roadmap.
Risk assessment and risk treatment are core parts of an ISO/IEC 27001 ISMS. Organizations determine which information-security risks require treatment and select appropriate controls. The Statement of Applicability documents the selected controls, their applicability and implementation status, including the rationale for exclusions where applicable.
The timeline varies with the ISMS scope, organization size, number of locations, existing controls, documentation maturity, risk profile and audit readiness. A focused organization with an established security program may progress faster than an organization building its ISMS from the ground up. Certification-body scheduling is also a separate factor.
ISO 27001 certification cost depends on ISMS scope, organization size, locations, technology environment, existing security maturity, consulting effort and certification-body audit fees. Consulting and certification-body fees are separate cost components, so a scope-based assessment is more accurate than a generic fixed price.
Ready to Build an Audit-Ready ISMS?
Get a clear view of your ISO/IEC 27001:2022 readiness, information-security risks, documentation gaps and implementation priorities with support from Varutra's cybersecurity and GRC team in India.
Download ISO 27001 Whitepaper (Free)
We respect your privacy. Your information will be kept confidential and handled securely.