PA DSS V 3.2 to SUNSET by 2022
About PA DSS Formerly known as the Payment Application Best Practices (PABP), the Payment Application Data Security Standard (PA-DSS) is a global security standard that the Payment Card Industry Security Standards Council (PCI SSC) has created. It was implemented to offer definitive data standard for…
Privacy Now to be a Fundamental Right in India
Electronic data protection in India is currently governed by the Indian penal code, the information Technology Act 2000 – IT Act Amendment 2008, and therefore the Information Technology Rules, first introduced in 2011. The non-public Data Protection Act (PDPA) emerged from a Supreme Court ruling…
How we are successfully managing & delivering the Cybersecurity Services during COVID-19 situation?
By now, we all already went through COVID pandemic’s first wave. The second wave has started hitting the world. Though this was a completely new experience to almost all businesses, but a few got adversely affected and found it difficult to learn the new normal….

Web Cache Poisoning – Through Host Header Injection
Web cache poisoning is an advanced hacking technique through which an attacker can exploit the pattern or behavior of a web cache and server. But before comprehending what is web cache poisoning, we should understand web cache and its vulnerabilities. This will help us in…
Apache Struts-2 Exploited to Remote Code Execution
This blog is to describe my finding on a web-based application which is a very well-known vulnerability found on Apache Struts-2 Remote Code Execution (RCE). What is Apache Struts-2? Apache Struts is one of the popular open-source frameworks that are used mainly by banks…
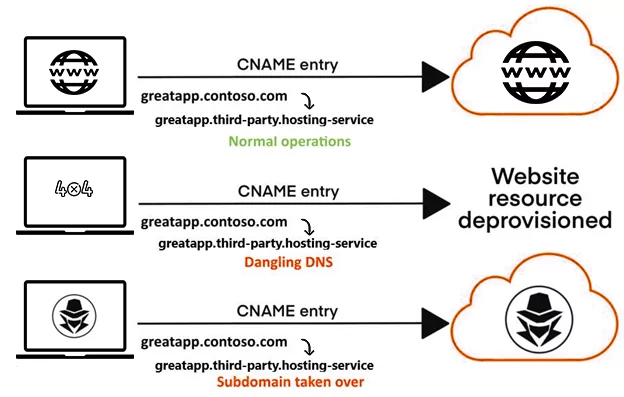
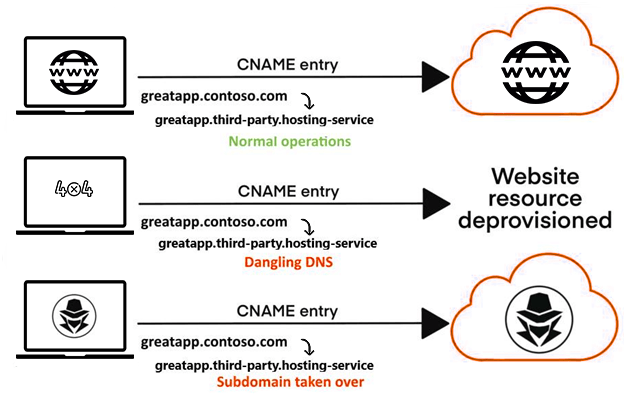
Subdomain Takeovers – CNAMEs And Cloud Services
Introduction A Subdomain Takeovers A hostile takeover of a subdomain by an attacker is known as a subdomain takeover. This issue mostly arises when organizations are integrating with either third-party hosting services or cloud service providers. The DNS records referring to these service providers remain…
Threat Modelling – Focused Defence for Modern Enterprises
Threat modeling is creating a buzz that everyone wants to talk about it. Every organization wants to remodel its overhaul information. It will help them in producing a priority list for security improvements for their requirements, concepts, design, and implementation. Overview of Threat Modelling…