AWS Pentesting – Part – 1
Nowadays, we have experienced many data breaches exposing different vulnerabilities like s3 buckets, compromised AWS cloud environments, and many more so avoid this it is important to perform AWS Pentesting. To understand the attacks on AWS, one must be aware of the different services…
MALWARE ANALYSIS – PART 2 (SETTING UP THE LAB)
In the previous blog, we have got a basic idea about Malware like what is malware, its behavior, types, and a brief introduction to Malware Analysis. In this section, we will be setting up the testing lab for dynamic and static analysis. So, let us…
HTTP Parameter Pollution
The parameter enables pages to load data from the back-end e.g., ID, search query. They make websites more interactive to the back-end as well as make them easy to use for visitors. Multiple parameters can be added with the help of special chars like (&,…
Communication Protocol – WebSocket Overview
What is a WebSocket? WebSocket is a Client-Server Bidirectional Communication protocol initiated over HTTP. WebSockets are used where there is continuous streaming of data over a network or where some real-time details are required by the application. Examples of such cases will be real-time web…
Introduction to Information Security Management System (ISMS)
What is an Information Security Management System ? An Information Security Management System (ISMS) is a set of policies and procedures for managing organizational confidential data and help to segregate data (Confidential/Restricted/General, etc.) of the organization. ISMS helps to manage security controls and risk across…
HTTP Request Smuggling
What is HTTP Request Smuggling? HTTP Request Smuggling is a vulnerability that takes advantage of the misconfiguration in parsing one or more HTTP devices or entities that are in the data flow, between the user and the web server. Devices like cache server, proxy server,…
Risk Management
Every organization conducts risk assessment and mitigation in order to identify risks and minimize their impact via risk mitigation. However, risk assessment is highly crucial since risks not identified or wrongly identified would have a ripple impact on their mitigation as well. Hence correct identification…
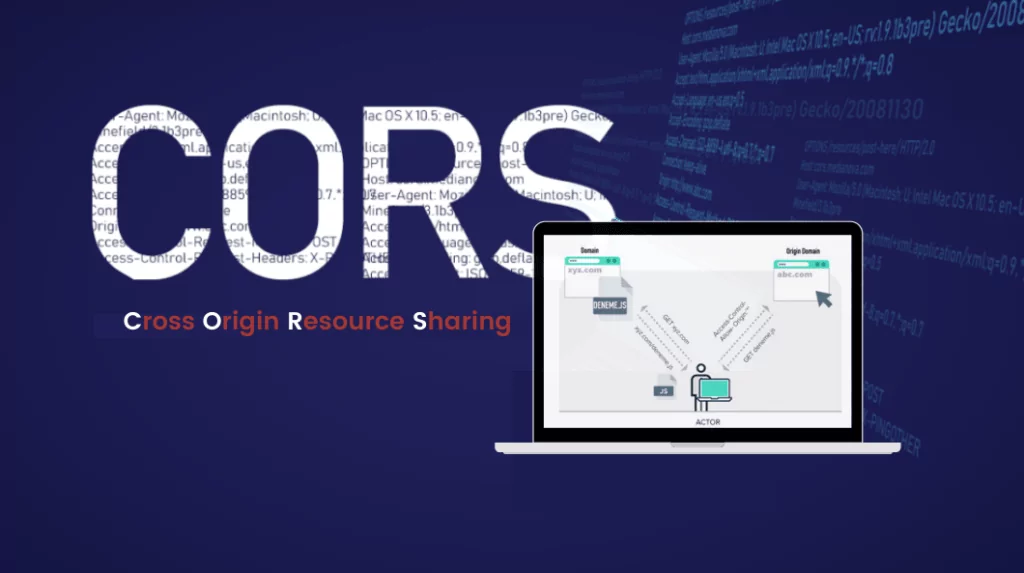
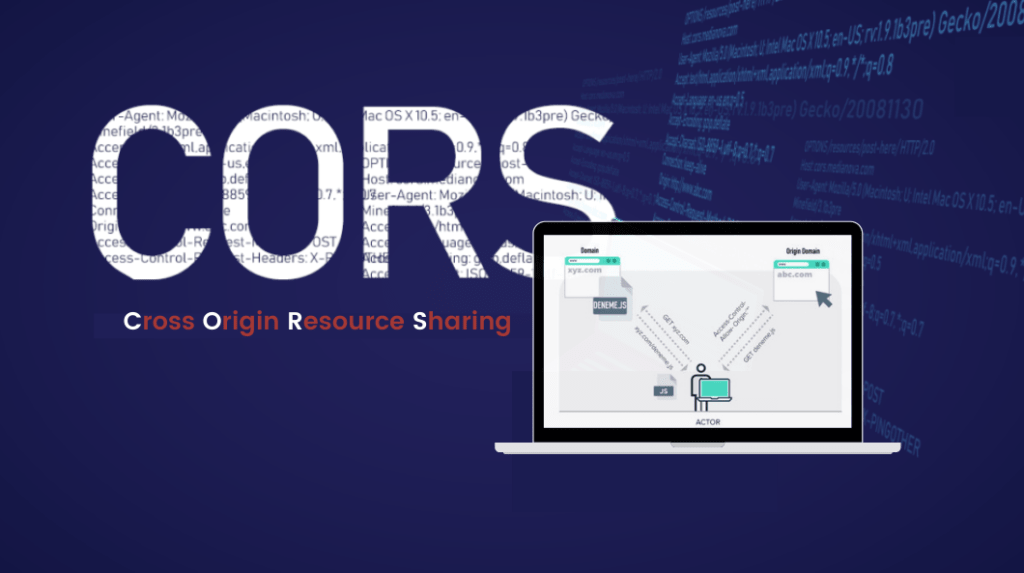
Misconfigured Cross-Origin Resource Sharing (CORS) Risk
The Cross-Origin Resource Sharing (CORS) is a mechanism to relax the Same Origin Policy (SOP) and to enable communication between websites, served on different domains, via browsers. Inside this blog, the reader will find: A brief introduction to the Same Origin Policy (SOP) and Cross-Origin…
Database Configuration Audit for Security and Compliance [Part-1]
Database Configuration Audit is the latest buzz word everyone is talking about and every organization wants to revamp their databases to produce and store a prioritized list of security improvements to the concept, requirements, design, or implementation. Overview Configuration Audit of a database includes…
Json web token (JWT) Attack – Most Common Scenarios
What is a JSON web token (JWT)? A JSON web token (JWT) token is an open standard which defines the compact and secure way of transmitting data or information as a JSON object between two parties. It is considered secure as it is digitally signed….