Formjacking – The New Favourite Cyber Crooks Hack
“We are in the most popular world of – Black hat hacker” What is Formjacking Attack? The year’s rampant threat in cybersecurity is Formjacking attack. It is a malicious injection of JavaScript code where the attacker is hacking a site and taking over them from…
Best Practices – BYOD and Mobile Device Security
BYOD (Bring Your Own Device) is a practice where employees can bring their own devices such as laptops, tablets or USB drives to the workplace. These devices belong to the employees or are sometimes approved for corporate use by the company which provides the support…
Code Obfuscation
Abstract In this paper, we came up with a basic understanding of Code Obfuscation – A Code Protection Technology which need anti-reverse engineering transformations to change programs in such a way that tools and approaches for program analysis become ineffective. What is Code Obfuscation?…
Vulnerabilities Related to SAML [Security Assertion Markup Language] – Part 1
In this blog, we are going to discuss about what is the SAML (Security Assertion Markup Language) and how it works as well as we are going to discuss the Security Assertion Markup Language Vulnerabilities. In the second part of this blog we will see…
Security Advisory – Typosquatting
There are multiple cases of redirect which are due to typing mistake (typos) from the users which leads to the threat of getting infected with cryptomining malwares, malware alerts, misleading messages, spams, etc. Such type of human typing error is called as Typosquatting. Typosquatting, also…
Best Practices to Harden Office 365
Here are some best practices to harden office 365 and ensure your data remains protected. 1. Password Policy It is always recommended to use a strong password policy to help secure the data and service access. In Office 365 for cloud-only users and active directory…
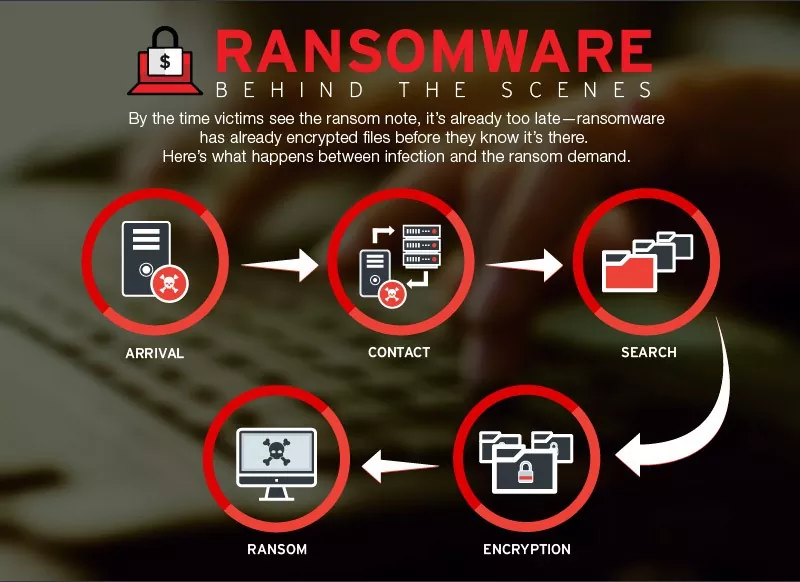
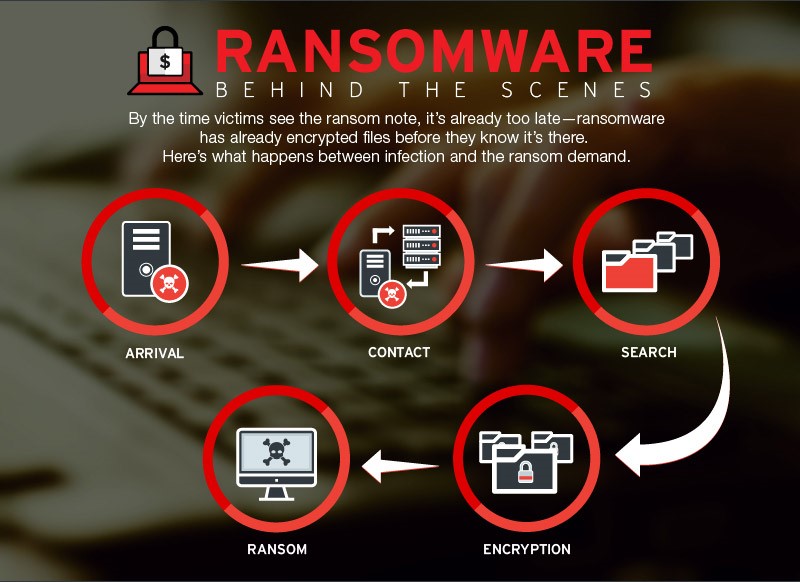
Security Advisory – Ransomware Attack Targeting China – December 2018
Ransomware Attack Targeting China – Security Advisory 1. Ransomware through Supply Chain Attack: A new ransomware strain spreading as a result of supply chain attack targeting Chinese users starting from December 1 and infected more than 100,000 computers. The ransomware not only encrypting the system…
Security Advisory – Tecnimont Cyber Theft
Tecnimont Cyber Theft – Security Advisory Background: Maire Tecnimont SpA is the parent company of the Italian group Maire Tecnimont, which consists of at least 50 operating companies in the engineering and main contracting sector. It deals in oil and gas, chemicals and petrochemicals,…
Security Advisory – Saipem Cyber Attack by Shamoon Malware
Saipem Cyber Attack by Shamoon Malware 1. Introduction Saipem identified cyber-attack on Monday i.e. on 10th December 2018 that had primarily affected its servers in the Middle East. The cyber-attack hit servers based in the Middle East, India, and Aberdeen and in a limited way…