Application Security: Risks and Best Practices
Applications play a crucial role in our lives as we use them for various useful purposes, ranging from shopping, interacting with people, managing finances, etc. Applications hold sensitive personal information (SPI), including our credit/debit card details, personal characteristic information, addresses, and so on. This makes…
Security Threat Intelligence Standards – STIX and TAXII
Introduction: Security Threat Intelligence Standards (STIX and TAXII) make day-to-day SOC operations go uninterrupted with a shared strategy that provides a collaborative response to cybersecurity threats. MITRE is one such organization that collaborates with industry and government institutions to develop a common approach towards cybersecurity…
Code Injection Vulnerabilities
Introduction to Code Injection Vulnerabilities Code injection is an attack where the attacker tries to inject a code that can be interpreted and executed by the application. Poor handling of data is responsible for the occurrence of this exploitation. It also means that when the…
Penetration Testing Using Metasploit Framework
Metasploit Framework is a powerful open-source penetration testing framework. You get to know all the information about penetration testing, IDS signature, and software vulnerabilities. It allows the execution and development of the exploit code against a remote target tool. Metasploit is not illegal itself, but…
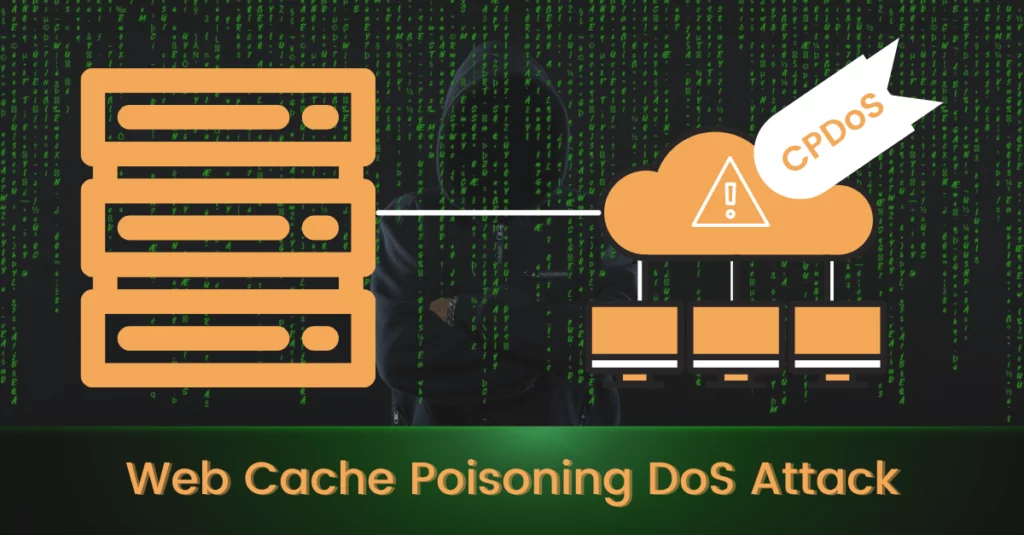
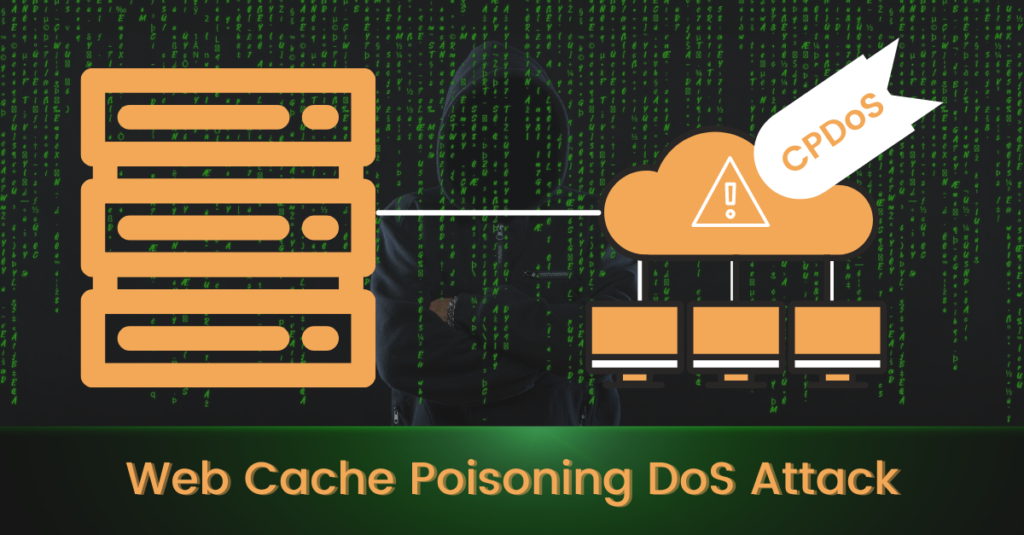
Web Cache Poisoning DoS Attack
The Web Cache Poisoning DoS Attack, also known as CPDoS. It is a type of DoS attack that primarily relies on the webserver’s cache mechanism. Overview As we can see that the modern web application’s HTTP servers consist of Front-end and Back-end servers. Front-end…
Android Weak Host Validation
In this blog we are going to discuss about android weak host validation and see how android application is not validating weak host for the android apps. Requirements: ADB (Android Debug Bridge) JADX (Android Decompiler) Android Emulator (Genymotion) For the testing purposes, we are using…
NoSQL Injection Vulnerability
In this blog, we will be discussing the NoSQL Injection Vulnerability and its exploitations scenarios. Before getting into the details of NoSQL injections, let us first see the difference between SQL (Structured Query Language) and NoSQL (Not Only Structured Query Language) databases. There are multiple…

Dark Web Ads Offering Access to Corporate Networks
The rate of cybercrime increased in the first half of 2020 due to the pandemic. The total volume of cyber attacks increased by 35% when compared to the second half of 2019, as per the September 2020 Microsoft Report on the increase in cyber threats….
Hibernate Query Language (HQL) Injection
HQL is the abbreviation for Hibernate Query Language. Hibernate can be classified as ORM or Object-Relational Mapping. It maps class definitions with similar SQL tables that are present within the source code. It is an object-oriented query language that is similar to SQL. However, it works…
WebSocket Vulnerabilities
This blog is about different types of WebSocket Vulnerabilities/Findings. So, we will be discussing different types of flaws that may exist in WebSockets. WebSockets are becoming more and more popular these days because of the simplicity they provide for the communication between the client and…