What Makes Penetration Testing Impactful – Post Exploitation
As a penetration tester, we often come across this riddle – What Makes Penetration Testing Really Impactful. As per penetration testing methodology – we identify vulnerability, prioritize the vulnerability considering the criticality of impacted assets, we obtain/modify/create an exploit, compromise the target system and we…
Beware Android Users – CLOAK AND DAGGER is here to exploit you
The WORLD has still not got over with the WannaCry ransomware menace and here comes one more android ransomware – Cloak and Dagger! People have been debating for years over Android V/s iPhone. It’s the ultimate battle. And it’s not ending anytime soon. But there…
Buffer Overflow Attacks
Introduction to Buffer Overflow Buffer is a storage place in memory where data can be stored. It’s mostly bound in a conditional statements to check the value given by the user and enter it in to the buffer and if the value entered by user…
Threat Advisory Report on WannaCry Ransomware (Critical Severity)
Here we will discuss Threat Advisory Report on WannaCry Ransomware (Critical Severity). 1. Introduction On Friday, May 12, countless organizations around the world began fending off attacks from a ransomware strain variously known as WannaCrypt, WanaDecrypt and Wanna.Cry. Security researchers found “WannaCry” or “WannaDecryptor”; a…
How To Develop Secure Software – Action Plan To Make Secure
The purpose of this article is to help to develop secure software. Easily avoided software defects are a primary cause of commonly exploited software vulnerabilities. By identifying insecure coding practices and developing secure alternatives, software developers can take practical steps to reduce or eliminate vulnerabilities…
Mobile Vulnerability Database (MVD)
Mobile Vulnerability Database, or MVD, is a unique place to find out about vulnerabilities reported worldwide for Mobile Platforms. Introduction to Mobile Vulnerability Database: The Android operating system is the most widely used operating system for mobile devices. Android has around 82.8% (IDC) market share…
Introduction to Secure Software Development Life Cycle
The most effective way to reduce application security risk is to implement a formal development process that includes security best practices to avoid application vulnerabilities. Secure Development process and Security Testing are powerful tools to monitor and search for application flaws and they should be…
External Penetration Testing – Case Study
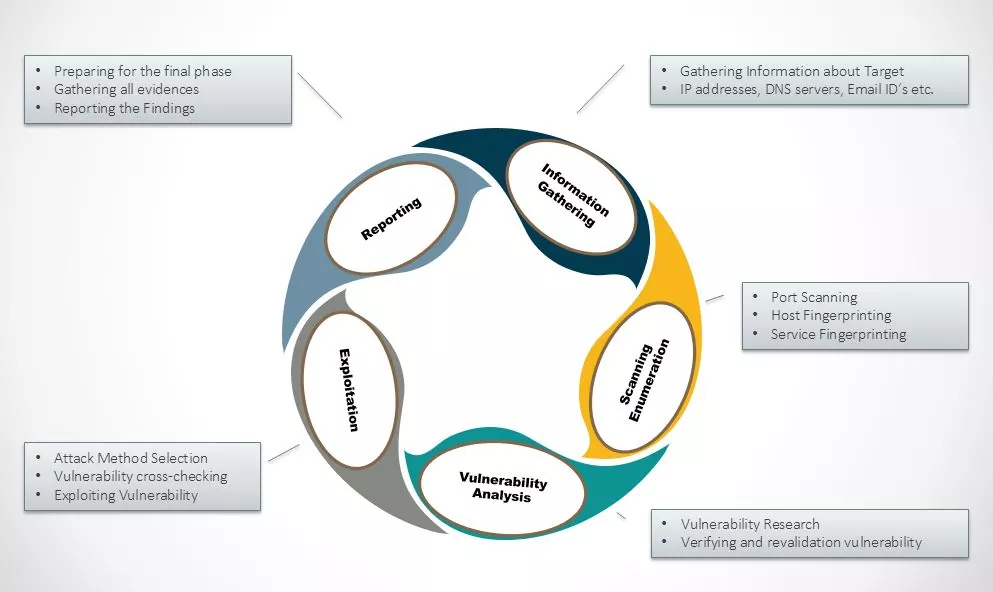
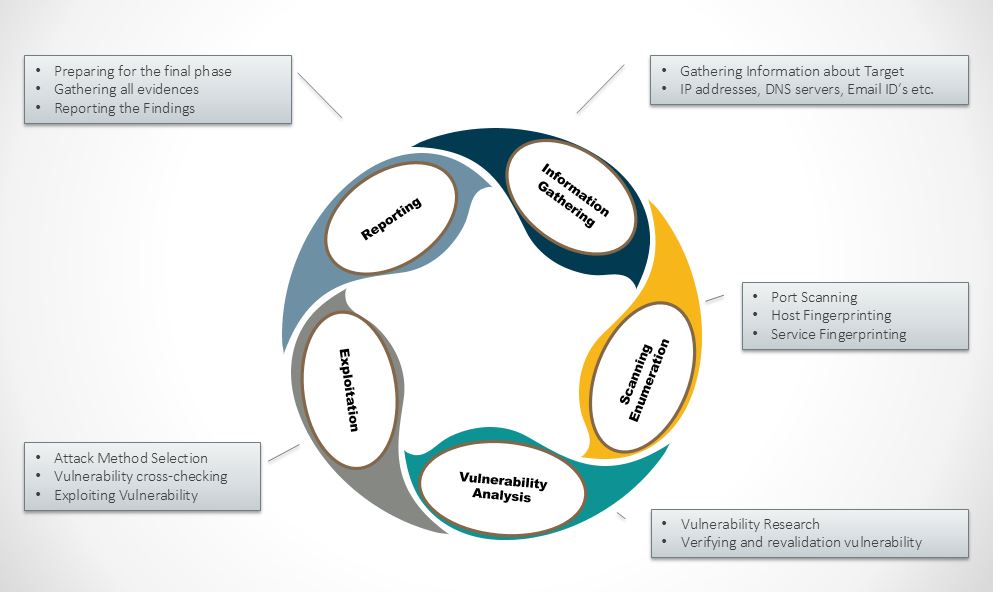
ABSTRACT External Penetration Testing consists of a reviewing and assessing the vulnerabilities that could be exploited by external users/Hacker without any credentials or without having any access to target system. The assessment basically plays vital role in ensuring perimeter security, infrastructure security of the organization…
Shell Shock – The Bash Vulnerability
BASH (Baurne Again Shell) Bash is the shell, or command language interpreter, that will appear in the GNU operating system. Bash is an sh-compatible shell that incorporates useful features from the Korn shell (ksh) and C shell (csh). It is intended to conform to the…
Android Malwares – An Overview
Malware, short for malicious software, is any software used to disrupt computer operation, gather sensitive information, or gain access to private computer systems. It can appear in the form of executable code, scripts, active content, and other software. ‘Malware’ is a general term used to…